Compliance,
attested.
Varman turns compliance into something that proves itself: continuous monitoring, built-in penetration testing, and AI governance on one control set. Always audit-ready, never a fire drill.
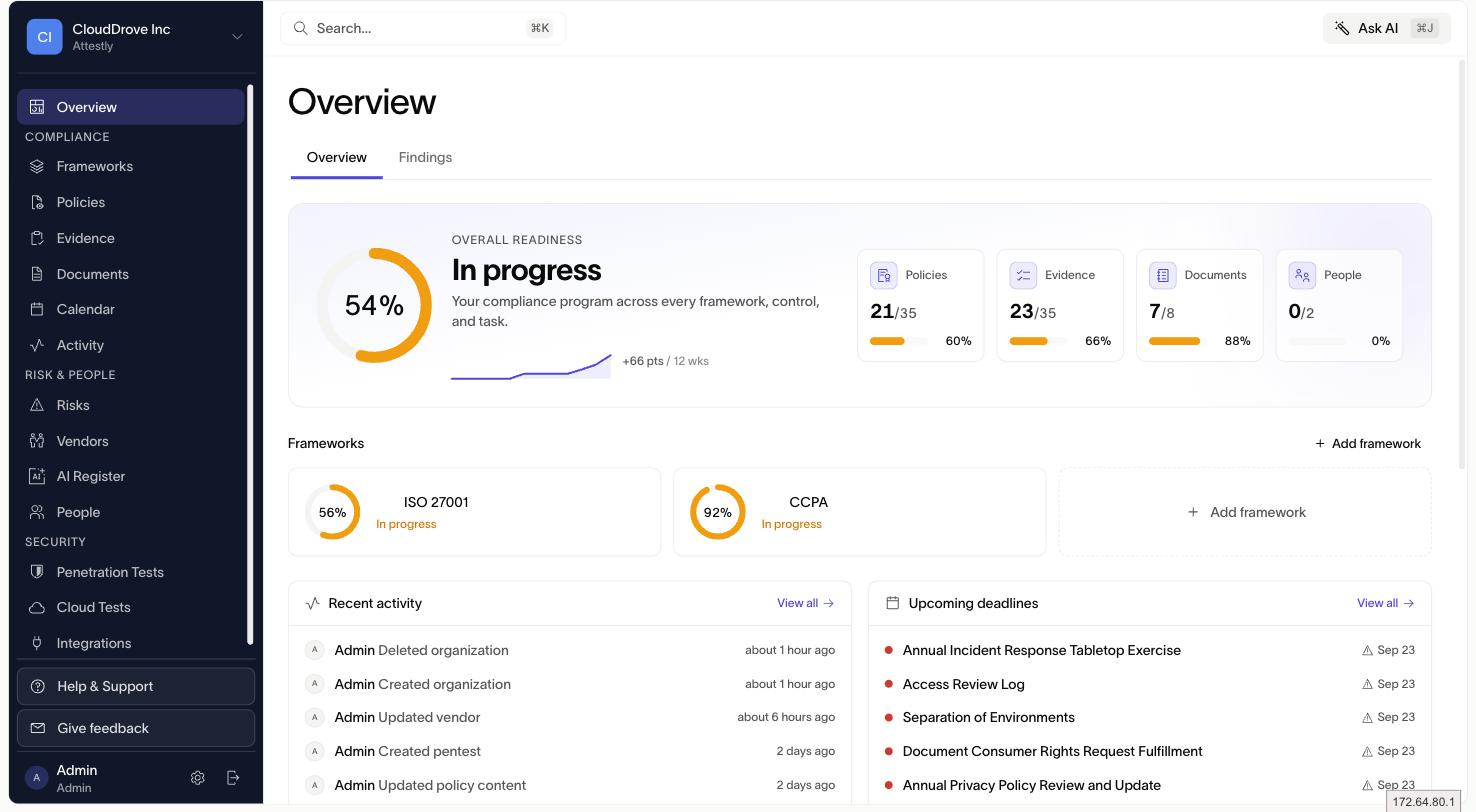
Connects to the stack you already run
Stop stitching a tool to every framework.
Evidence, monitoring, pentesting, and AI governance share one data model, so adding a framework is a mapping, not a migration.
Automated evidence
Connect your stack and evidence collects itself, mapped to every framework you run.
Continuous monitoring
Checks run on a schedule. Drift and failing controls surface the day they happen.
The compliance agent
Ask in plain language. The agent answers from your own program data.
Trust Center
Publish a live security page so review stops blocking deals.
Every control counts toward every framework.
Satisfy a control once and it applies everywhere it is referenced. Watch readiness climb per framework as evidence lands, with a clear view of what is met and what remains.
Browse frameworks →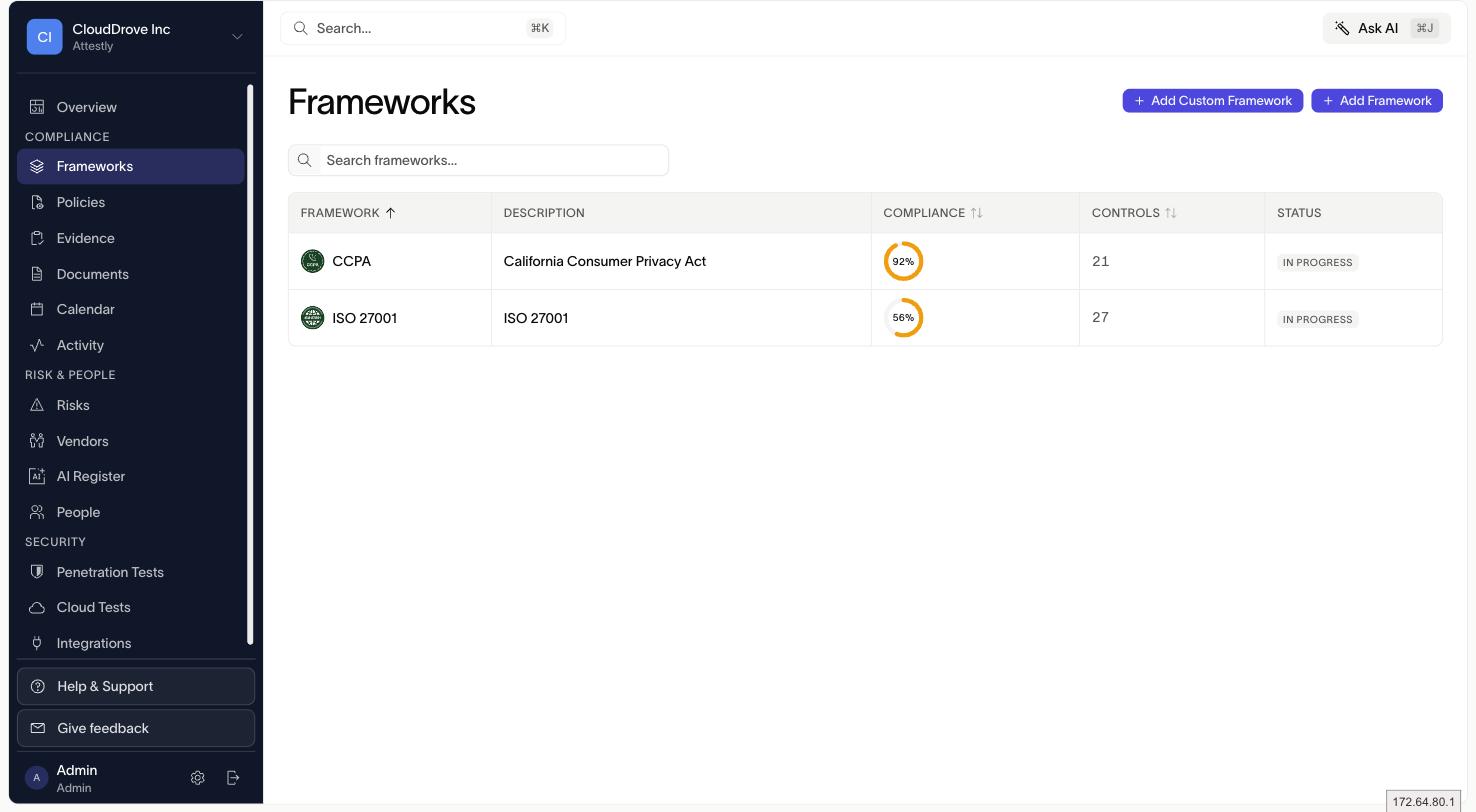
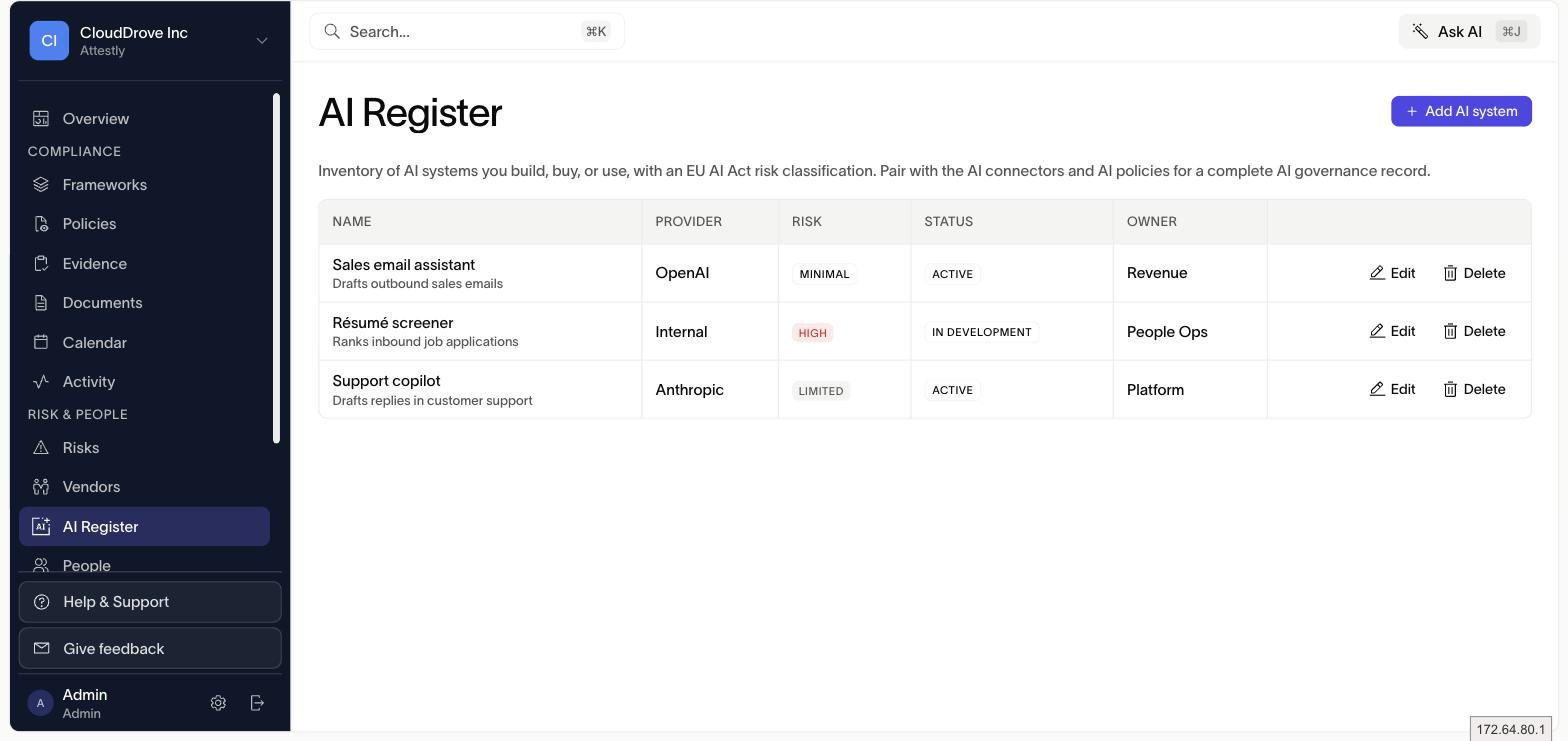
Govern the AI you build and the AI you buy.
Every AI tool your team adopts is a new risk and a new audit question. Varman keeps an AI System Register, classifies each system against EU AI Act risk tiers, and ships policy AI policy templates alongside the ISO 42001 framework.
- AI System Register with owner, purpose, and lifecycle
- EU AI Act risk tiers: unacceptable, high, limited, minimal
- Connectors that inventory OpenAI and Anthropic access
- ISO 42001 framework and AI policy templates
Penetration testing inside the platform.
Run pentests on demand or on a schedule. Findings flow straight into your evidence and become remediation tasks, so a test improves your posture instead of producing a PDF that goes stale the day it lands.
Latest test · ReconX
Complete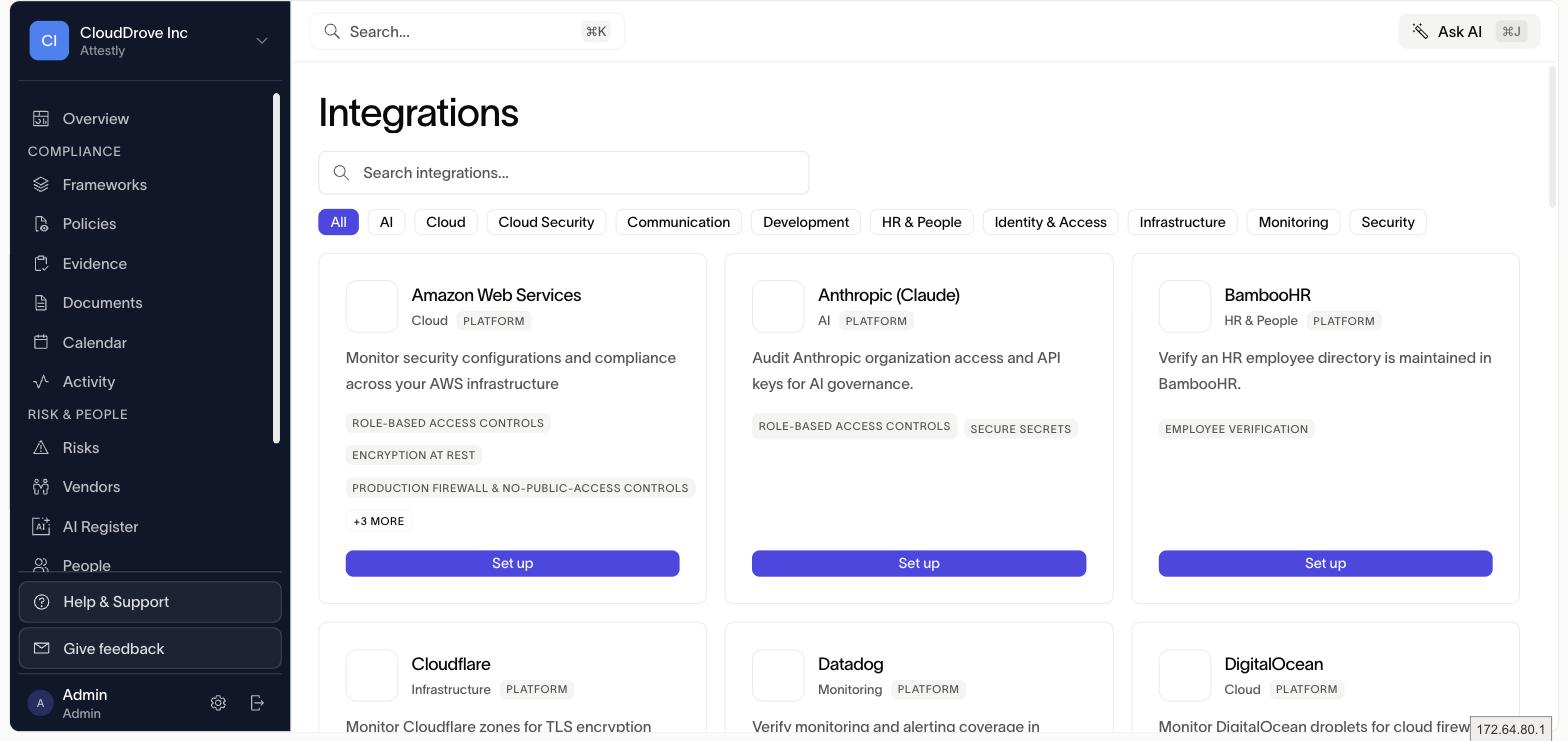
Connects to the stack you already run.
Cloud, code, identity, HR, monitoring, and your AI providers. Self-serve credentials, continuous checks, evidence mapped to controls automatically.
Browse all integrations →Four steps, then it runs on its own.
- 01
Connect
Link cloud, identity, code, and HR with native integrations.
- 02
Map
One control set maps across SOC 2, ISO 27001, GDPR, HIPAA, and ISO 42001 at once.
- 03
Monitor
Evidence collects on a schedule. Failing controls and stale tasks surface on their own.
- 04
Attest
Hand auditors a clean, current evidence room, pentest findings and AI risk included.
Get audit-ready, and stay that way.
See how Varman automates your frameworks, pentests, and AI governance in one place.