One platform for compliance, security, and AI risk.
Most teams run a GRC tool, a separate pentest vendor, and a spreadsheet for AI risk. Varman puts all three on one data model, so evidence, findings, and AI systems reinforce each other.
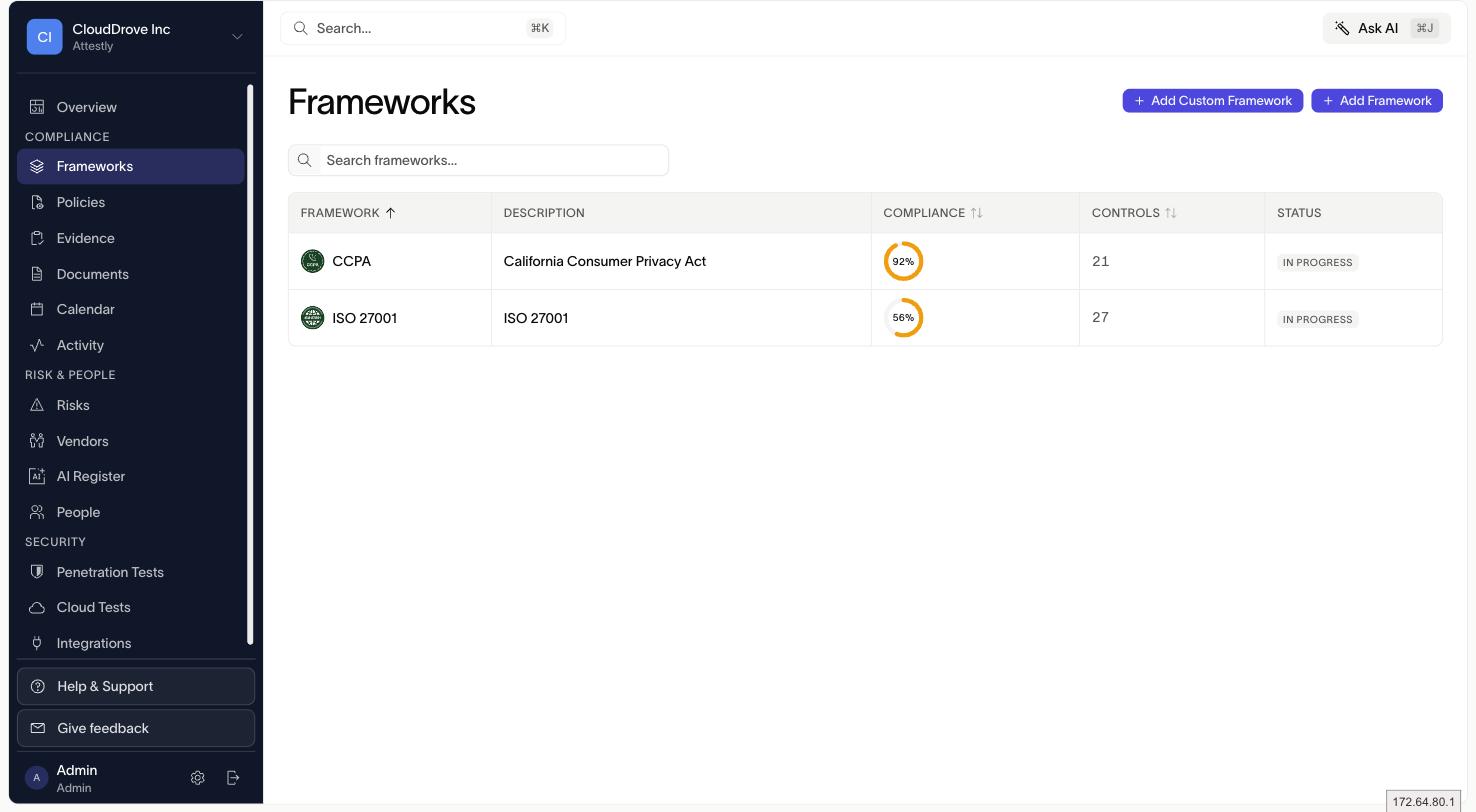
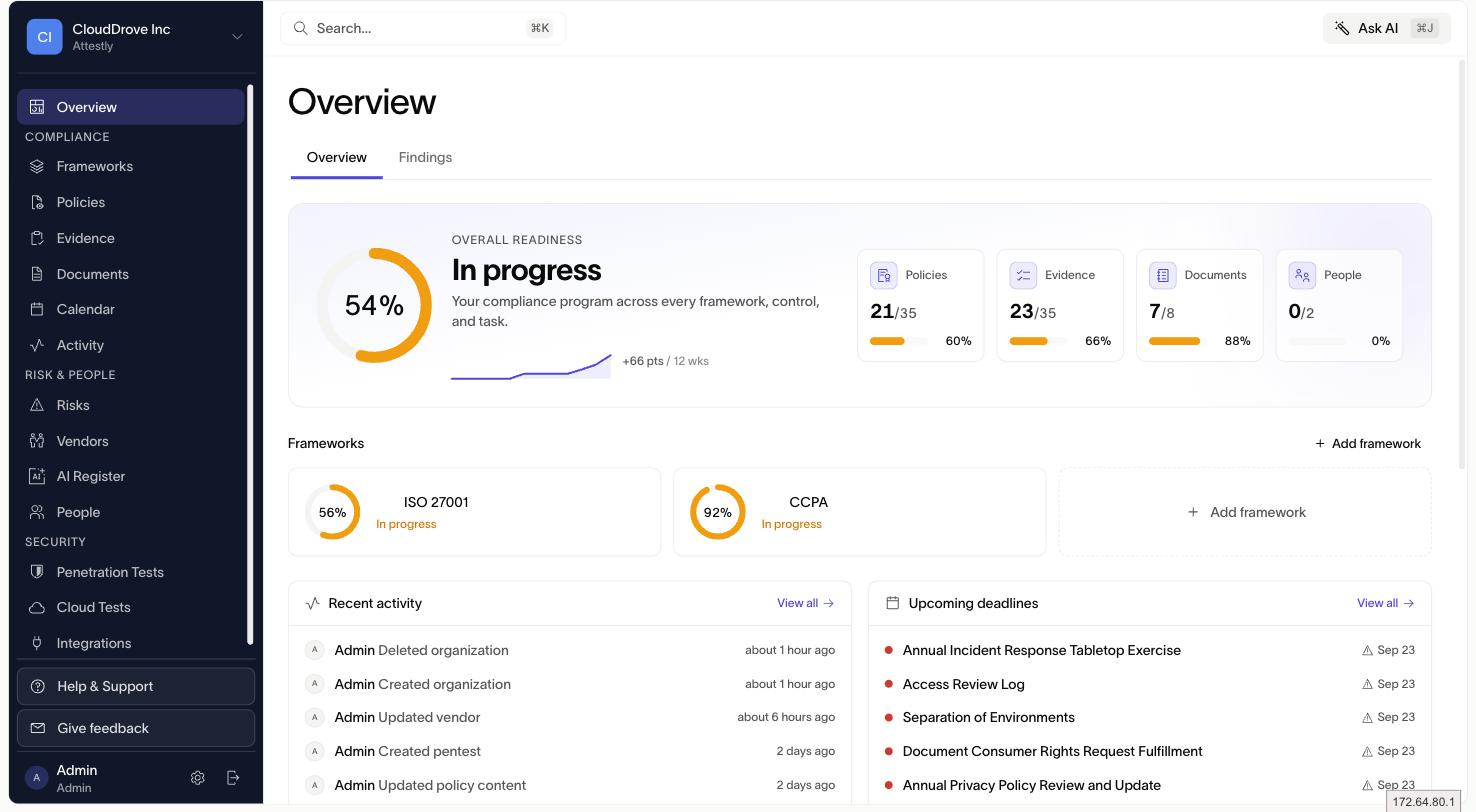
Collect evidence once, satisfy every framework.
Varman maps a single control set across all your frameworks. Connect a source and its evidence flows to each control that needs it, so SOC 2 and ISO 27001 share the same proof.
- One control set, many frameworks
- Evidence tied to controls automatically
- Readiness tracked per framework
Checks that run on a schedule, not once a year.
Integration checks re-run continuously and compare live configuration against your controls. When something drifts, the failing check shows up against the control it affects.
- Scheduled re-checks across the stack
- Failing checks shown against controls
- Results kept as evidence
Pentests that feed your compliance evidence.
Run a penetration test on demand or on a recurring schedule. Findings land as tracked issues, link to the controls they affect, and become remediation tasks.
- On-demand or scheduled runs
- Findings become remediation tasks
- Linked to affected controls and evidence
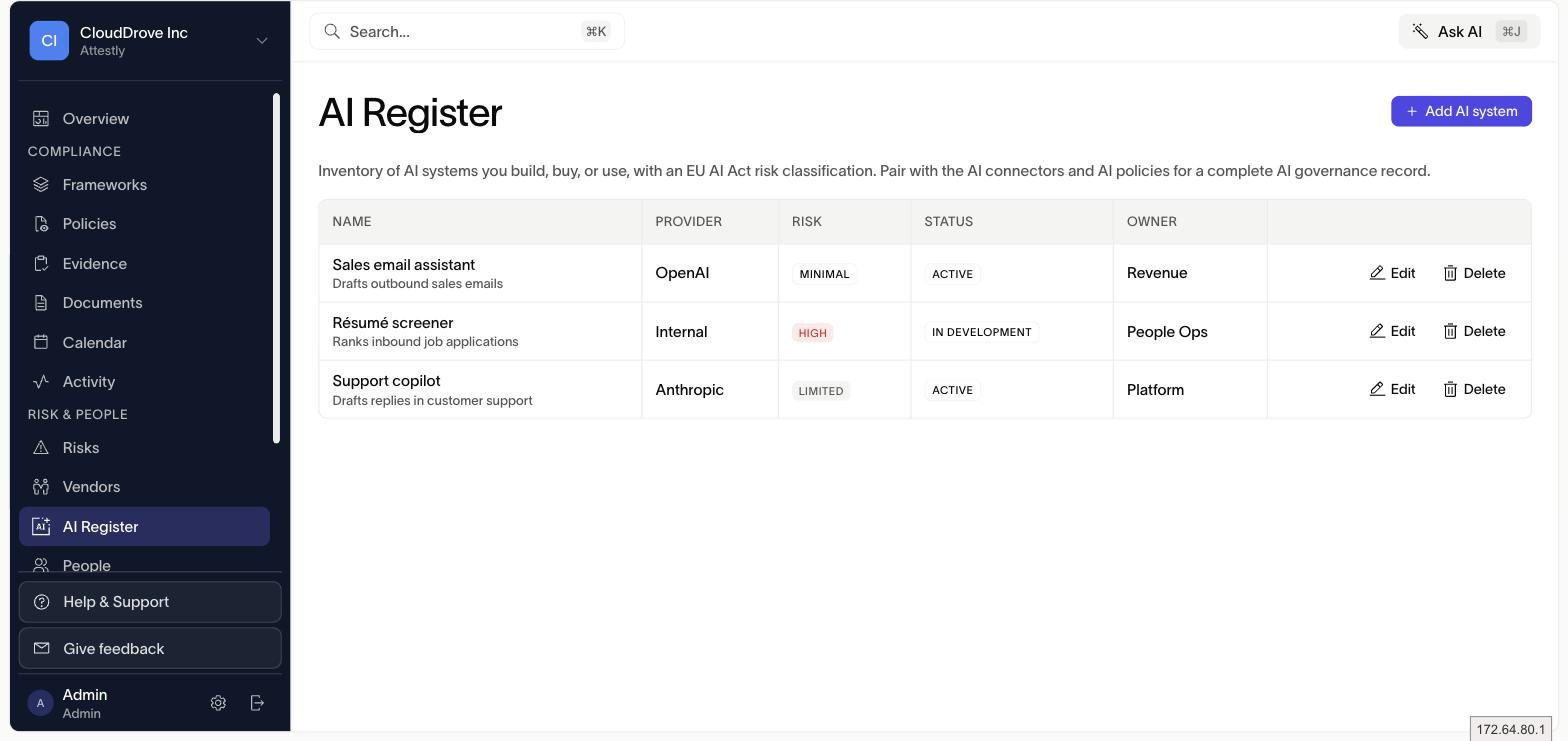
Govern the AI you build and the AI you buy.
Keep an AI System Register of every model and tool in use, classify each against EU AI Act risk tiers, and adopt the ISO 42001 framework with AI policy templates. Connectors inventory OpenAI and Anthropic access.
- AI System Register with risk tiers
- ISO 42001 framework and AI policy templates
- OpenAI and Anthropic connectors
Share your posture, shorten security review.
Publish a live Trust Center backed by real-time control status. Prospects self-serve your certifications and security details, and questionnaire answers draft themselves from your own evidence.
- Live, self-serve security page
- Backed by real control status
- Questionnaire answers drafted from evidence
Ask your compliance program a question.
The built-in agent reads your policies, risks, tasks, findings, vendors, and AI register. Ask what is overdue, which controls are failing, or what changed, and get an answer grounded in your own data.
- Grounded in your live program data
- Reads policies, risks, tasks, findings
- Plain-language answers, scoped by permission